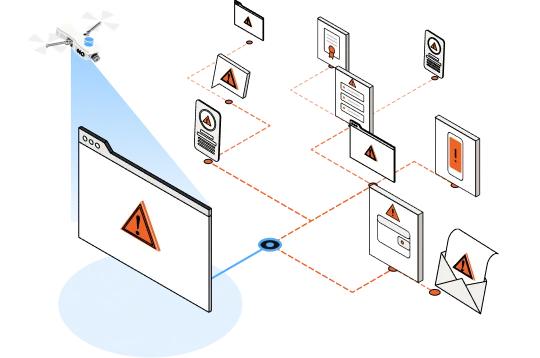
Less noise, deeper investigations
Outtake finds impersonations, investigates the network behind them and handles the takedown process, quickly and automatically learning your custom preferences to surface only alerts that matter.



Outtake and ZeroFox comparison
See how they stack up on each part of the takedown pipeline.
Threat coverage
Outtake
Deeper threat coverage: 90% of the web is non-text-based. Outtake's multi-modal threat detection identifies risks across any language in images, video, audio, and text to ensure the broadest coverage possible. Search agents get smarter as threats evolve, learning from every finding to uncover more. No FoxScript to request or analyst to wait on.
ZeroFox
Limited coverage: Despite stated image and video capabilities, ZeroFox often misses threats embedded in video when a keyword or name match isn't present. Alerting is still built on rules and name/keyword policies (pre-built policies plus custom "FoxScripts"), and tuning is done by people and can take weeks or months.
Relevant alerts
Outtake
Zero noise, only alerts that matter: Outtake's intelligent risk scoring filters out noise and surfaces hard-to-find threats. With every action and escalation, the platform adapts to your security and risk profile so you're not waiting on a response from manual bottlenecks. Outtake's TAM support partners with you to scale your program.
ZeroFox
Alert overload: ZeroFox users report tuning filters takes months to years, and the filters have difficulty adapting to a changing threat environment. Ongoing tuning is part of ZeroFox's manual service.
Deep investigations
Outtake
Faster deep investigations: Compress hours of investigations into minutes with Outtake. Uncover campaign infrastructure and the full attack network for broader mitigation (takedowns, blocking, escalations), making takedown requests more compelling and making it more painful for threat actors to re-target you.
ZeroFox
Surface-level and slow: ZeroFox has begun connecting related alerts but cannot investigate the open web automatically. Deeper investigations still rely on analysts working business hours, who can only follow a few leads at a time while a campaign has hundreds of connected pieces, resulting in reduced pattern recognition and hidden threats staying live.
Ease of use
Outtake
Works where you do: Outtake provides an API, an MCP, and an AI assistant in-app. Easily trigger takedowns on the go from Copilot or Slack. Ask questions about your data and trends. After filing, agents handle the provider back-and-forth and confirm removal.
ZeroFox
ZeroFox provides an API. Conversational intelligence and conversational takedowns are not built in. Cases are worked by analysts, which often means delays and repeat follow-ups.
Takedowns
Outtake
Fast, unlimited takedowns: Built to scale with any threat environment. Immediate enforcement across multiple reporting paths with automatic re-reporting until mitigation.
ZeroFox
Metered, slower: Capacity depends on your plan. Published bundles cover 250, 500 or 1,000 successful removals a year. Customers in calls and on G2 note that takedowns may take too long or remain incomplete.
When ZeroFox may be the better fit
If your priority is an analyst-led intelligence program with covert collection in closed communities, ZeroFox's dedicated analysts and DarkOps services deserve a close look. You can retain that coverage while evaluating Outtake for impersonation investigation and enforcement.
You don't need to “fine-tune” Outtake.
To get started with Outtake, just tell us what matters to you. Then, see coverage and takedown speed in a free pilot without commitment.
01
Tell us what matters
Share the brands, people, surfaces and threats you want covered.
02
We set up your free pilot
Your Outtake forward deployed engineer builds the profile from public data.
03
See coverage and takedown speed
Observe how Outtake catches more real threats. Evaluate the speed to takedown of Outtake vs ZeroFox on like-for-like threats.
How Outtake works
Outtake finds the threat, investigates the network behind it, builds the case and carries it through takedown. Your team has reduced alert fatigue, deeper analysis, and faster completed takedowns.
01 · Find
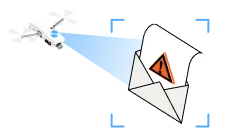
Find and check the threat
Search agents surface potential threats and check them against your brands, people and products.
02 · Investigate
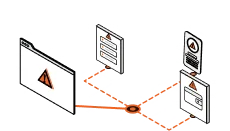
Follow the connections
From one malicious finding, agents follow certificates, analytics IDs, hosting and linked domains to the rest of the operation, including assets search engines never index.
03 · Build the case
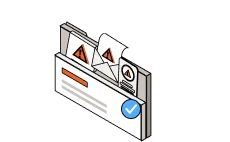
Submit robust case for takedown
Evidence is packaged with abuse categories platforms recognize (ex: XARF) and all malicious alerts are sent to the platform for removal.
04 · Take down and track
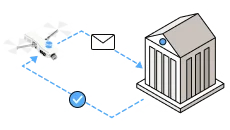
Handle back-and-forth
AI agents handle follow up, confirm removal and re-report returning threats. Updates reach you in your messaging app or your SIEM.
Why teams move ZeroFox workflows to Outtake
Buyers want reduced noise and faster resolutions.
“You guys are more expensive, but better.”
“That's what we're missing. The agentic part.”
“ZeroFox hasn't been AI native.”
“We are getting more detail from Outtake.”
“We had a bad experience with ZeroFox.”
“We just don't have the capacity to look at these hundreds of alerts that are coming in.”

Source: 2026 customer calls discussing ZeroFox
Case studies
Case study
Scicomm Media
Further readingThe Challenge
Stopping social media impersonation attacks during the podcast's explosive growth
The Result
Autonomous detection and takedowns that neutralize impersonations before they damage the brand
Case study
CashApp
Further readingThe Challenge
Fighting fraud on video-first platforms without scalable coverage
The Result
Detection that mirrors how analysts think without needing to watch every video manually
Case study
AppLovin
Further readingThe Challenge
Fending off modern social engineering attacks during moments of peak publicity
The Result
Always-on protection that finds and zaps digital impersonation before it causes real harm
Explore the full stories for each customer's use case, deployment and results.
Questions teams ask before switching
Yes. Request a threat report and talk to the team. We will set up your free pilot and help you plan and complete a transition if you decide to make the move.
Put us to the test: see what's behind a threat you already know
Bring a suspicious URL and we'll show you how Outtake maps the network behind it, follows the connections and builds the evidence. See the investigation on a real example before deciding whether to go further. No pilot needed.
Get a free threat report