
Phishing and cloned login portals
Lookalike domains and cloned client portals, removed along with the hosting behind them.

Dismantle the fraud campaign behind every impersonation of your institution
Cloned login portals and fake investment platforms run as coordinated operations. Outtake's Next-Gen DRP maps those connections and coordinates takedowns across the campaign.
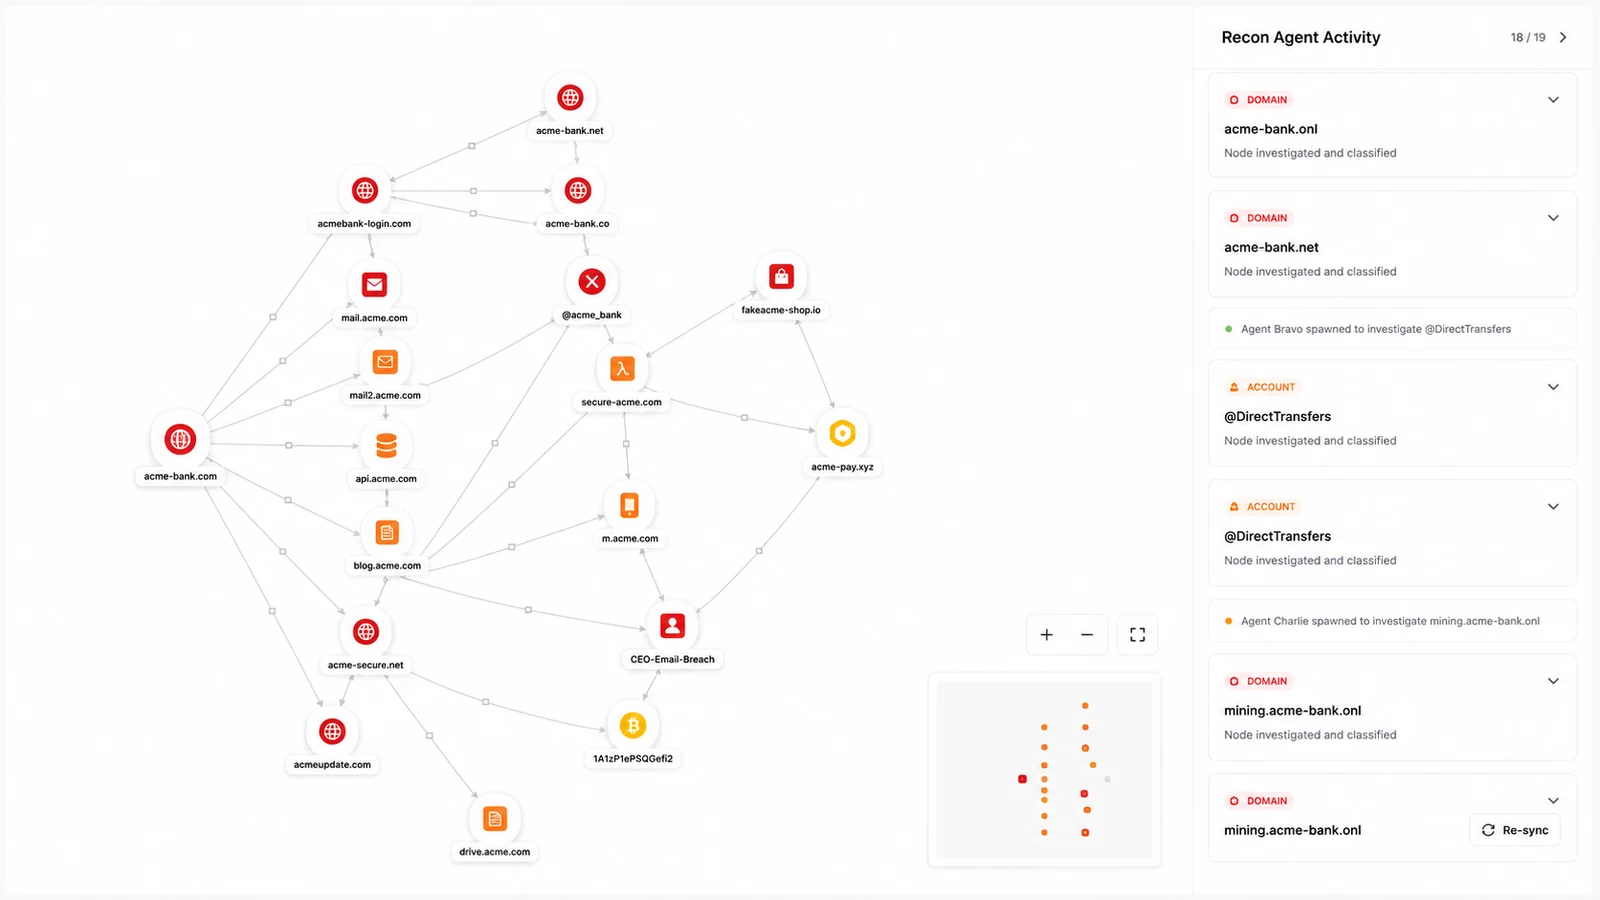


Next-Generation Digital Risk Protection (NGDRP) finds and removes scams that impersonate a financial institution outside its network, including cloned login portals, fake trading platforms, advisor impersonation, fraudulent ads and counterfeit apps. The Threat Graph links the domains, accounts and wallets behind each scam so analysts can investigate the campaign and remove connected assets together in hours.
Scammers borrow a trusted institution's identity to capture credentials, redirect payments and push fraudulent investments. Each convincing fake makes the next one easier to believe, and the assets below are built to work together.
Lookalike domains and cloned client portals, removed along with the hosting behind them.
Fraudulent trading portals and crypto schemes promoted through social profiles and messaging groups.
Fake profiles using the names and photos of your executives, advisors, brokers and agents.
Paid placements that send customers into fraudulent schemes, caught by visual match.
Counterfeit mobile apps and fake support accounts waiting for customers who need help.
Leaked credentials and wallet infrastructure that tie separate scams back to one operator.
Legacy digital risk protection was built for a slower attacker. Those tools match keywords and hand each alert to an analyst, who files takedowns one URL at a time.
Scammers stand up the replacement domain before that ticket closes, so the queue grows while the operation behind it keeps running.
Result: The visible asset comes down while the hosting, accounts and sister domains behind it stay live.
Result: Analysts remove the connected assets together, including the infrastructure the operators use to run the campaign.
Cloned login pages and fraudulent account alerts.
Scams that move fast across social and video platforms.
Fake advisors and cloned client portals.
Fake agents and fraudulent claims services.
Fraudulent loan offers and advance-fee schemes.
Fake exchanges and the wallet infrastructure behind them.
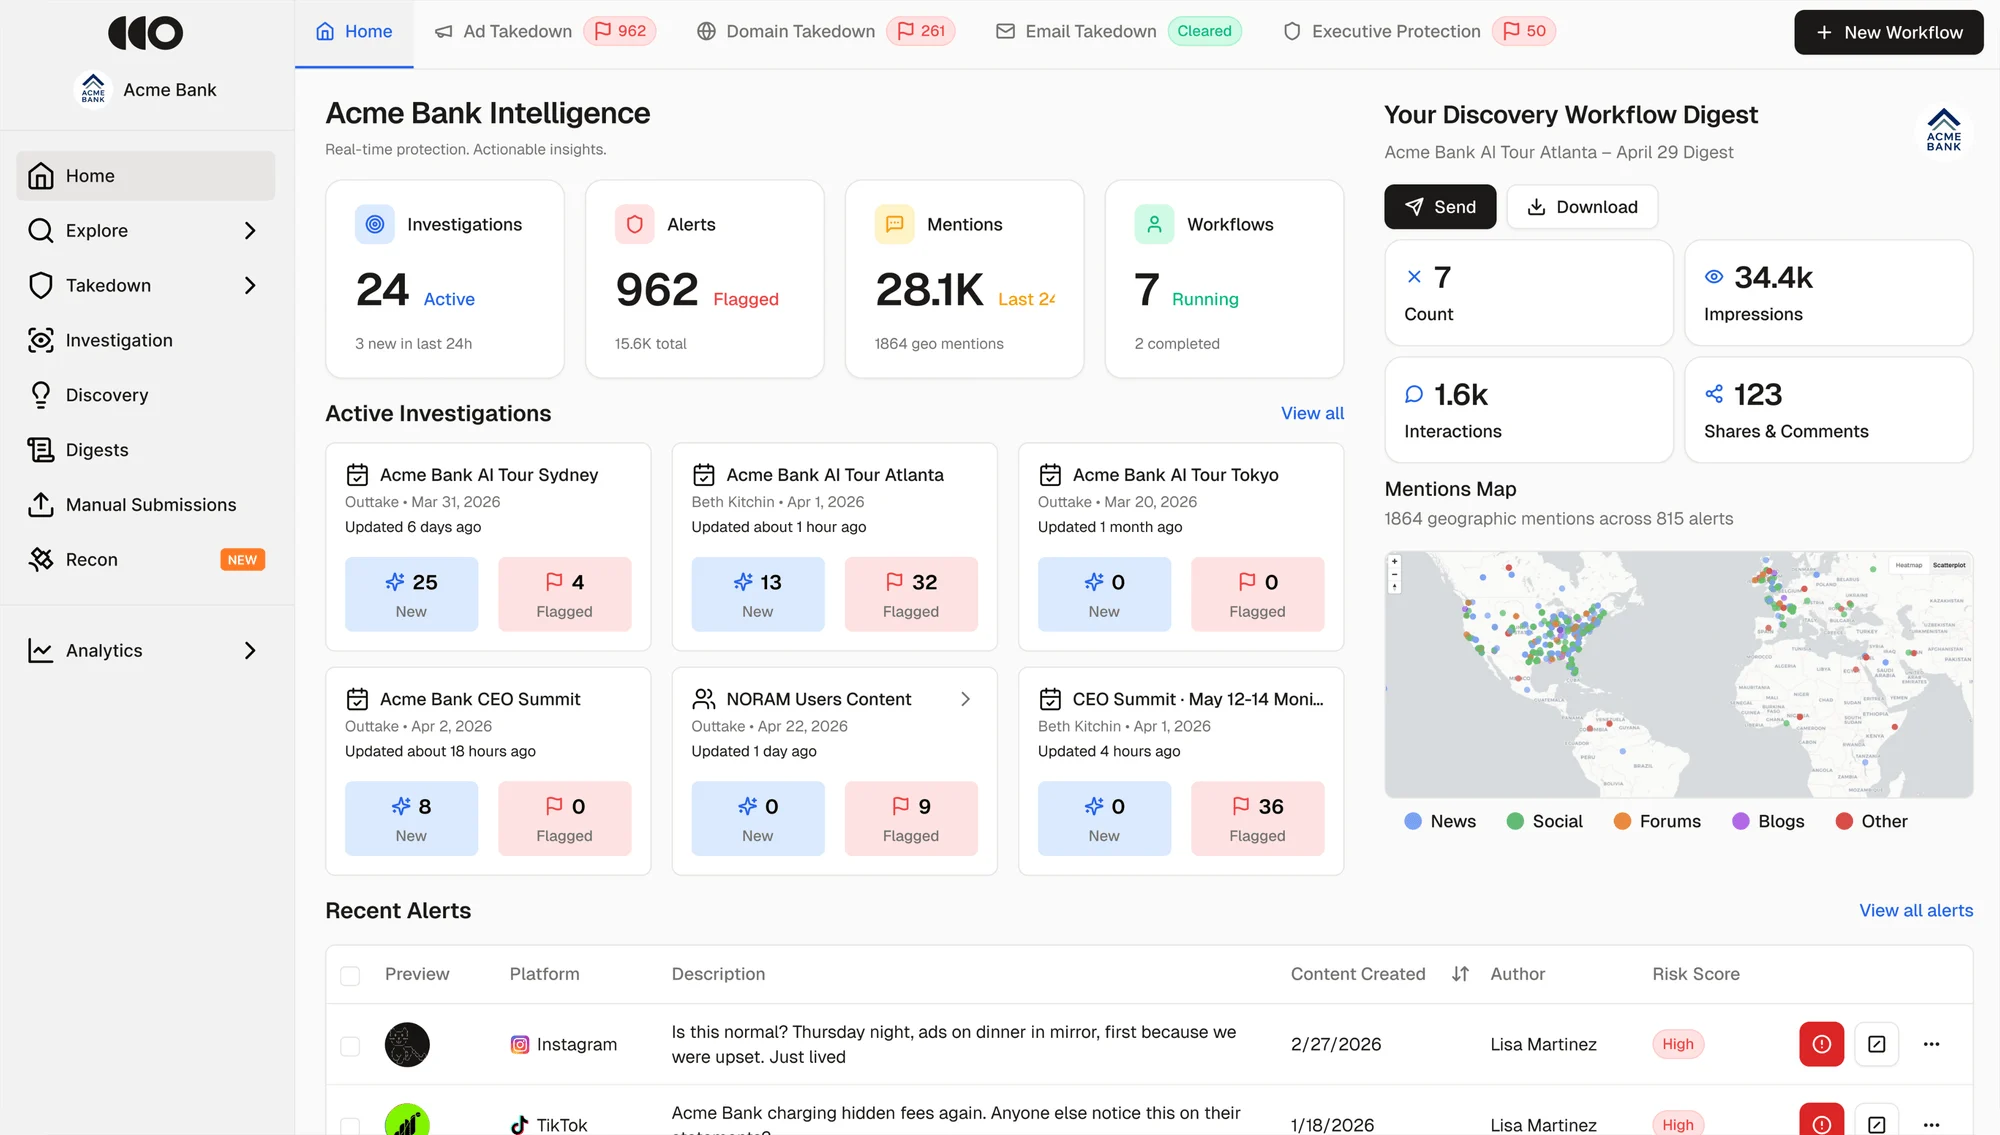
Register your brands, executives, advisors, domains and apps once. Outtake uses that record to identify impersonations.

Agentic Search reads logos, layouts, images, video and audio across monitored channels to distinguish brand mentions from active fraud campaigns. Recon Agent rescans every 16 minutes.
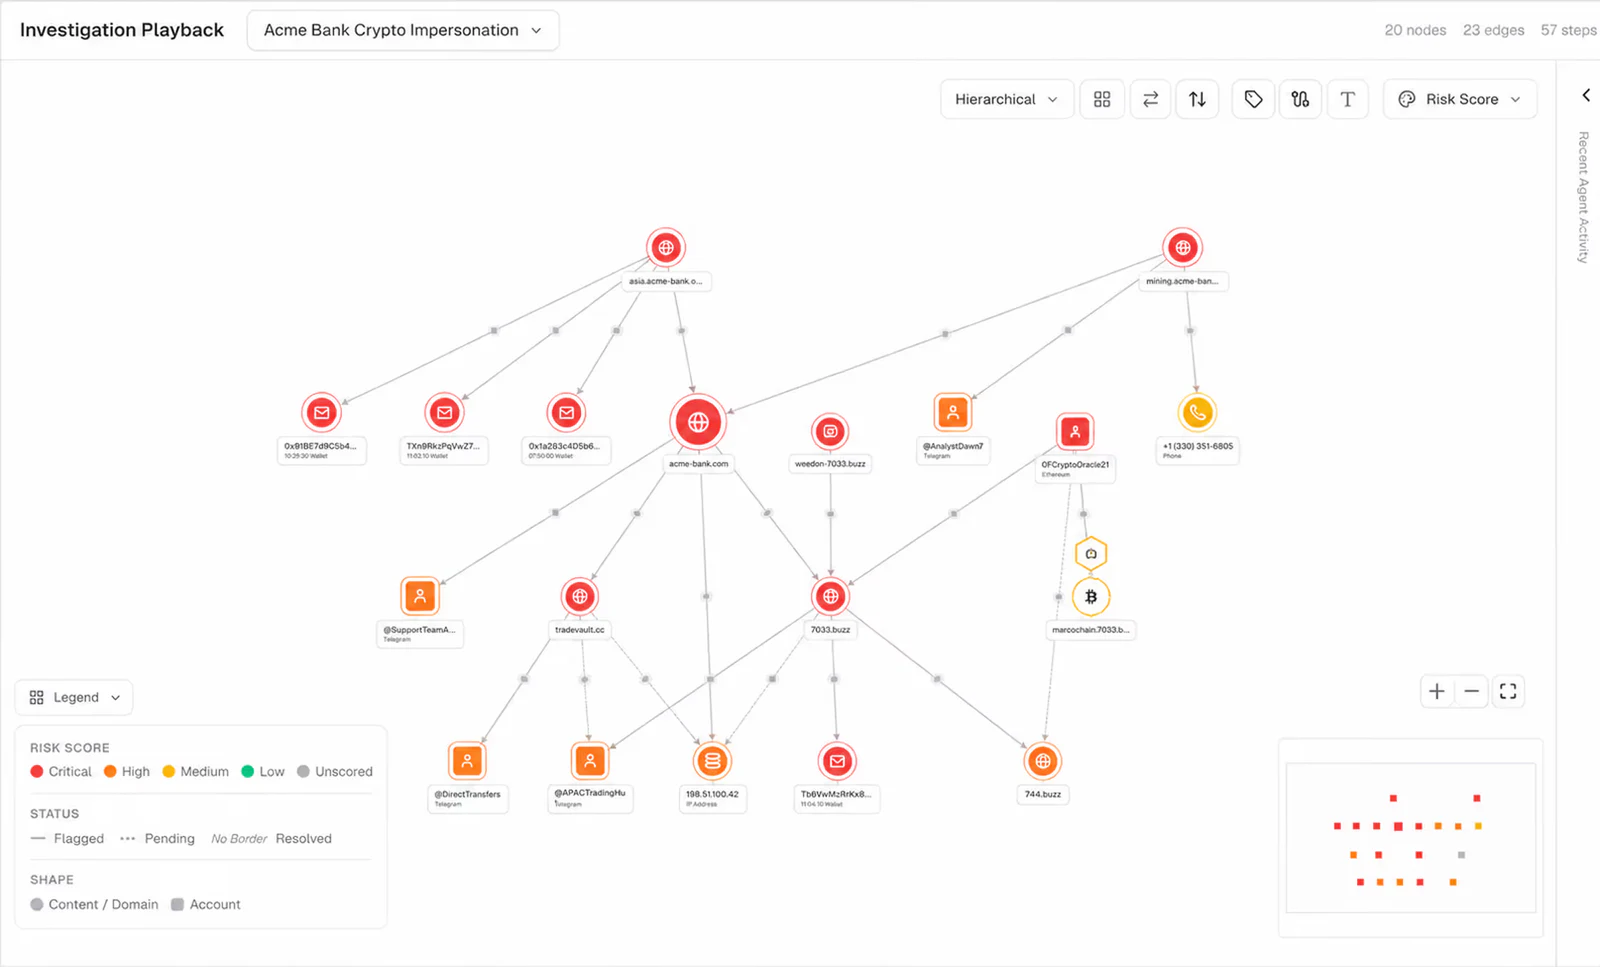
The Threat Graph links the spoofed domains, fake apps, ad accounts, chat groups and wallets behind each scam, so your analysts can investigate the connected assets in one case.

Outtake sends takedown requests to the registrars, hosts and platforms connected to a campaign in parallel. Removals take hours, with a 99.4% confirmation rate. Agents handle cases from discovery to removal without a queue, and analysts can track their progress.


takedowns confirmed
of social takedowns completed in under 24 hours
platforms, marketplaces and dark web sources indexed through Agentic Search
Recon Agent scan cycle
"Outtake gave us full visibility into every platform our customers are using and the proof to show leadership we're catching threats before they ever have the chance to spread."
"The 24 hour digest surfaced threats we missed on the feed of a different tool. We have been very happy with it."
"You just did what I spent all day yesterday doing, in five minutes. I can't think of enough good adjectives about this."
digital findings analyzed
abuse reports filed
takedowns completed
AGGREGATE PERFORMANCE FOR FINANCIAL SERVICES CUSTOMERS AS OF AUGUST 26, 2026
Watch how Outtake investigates a malicious signal to find the fake trading platform, social profiles, messaging groups and payment infrastructure behind a pig butchering campaign.
Explore pig butchering defense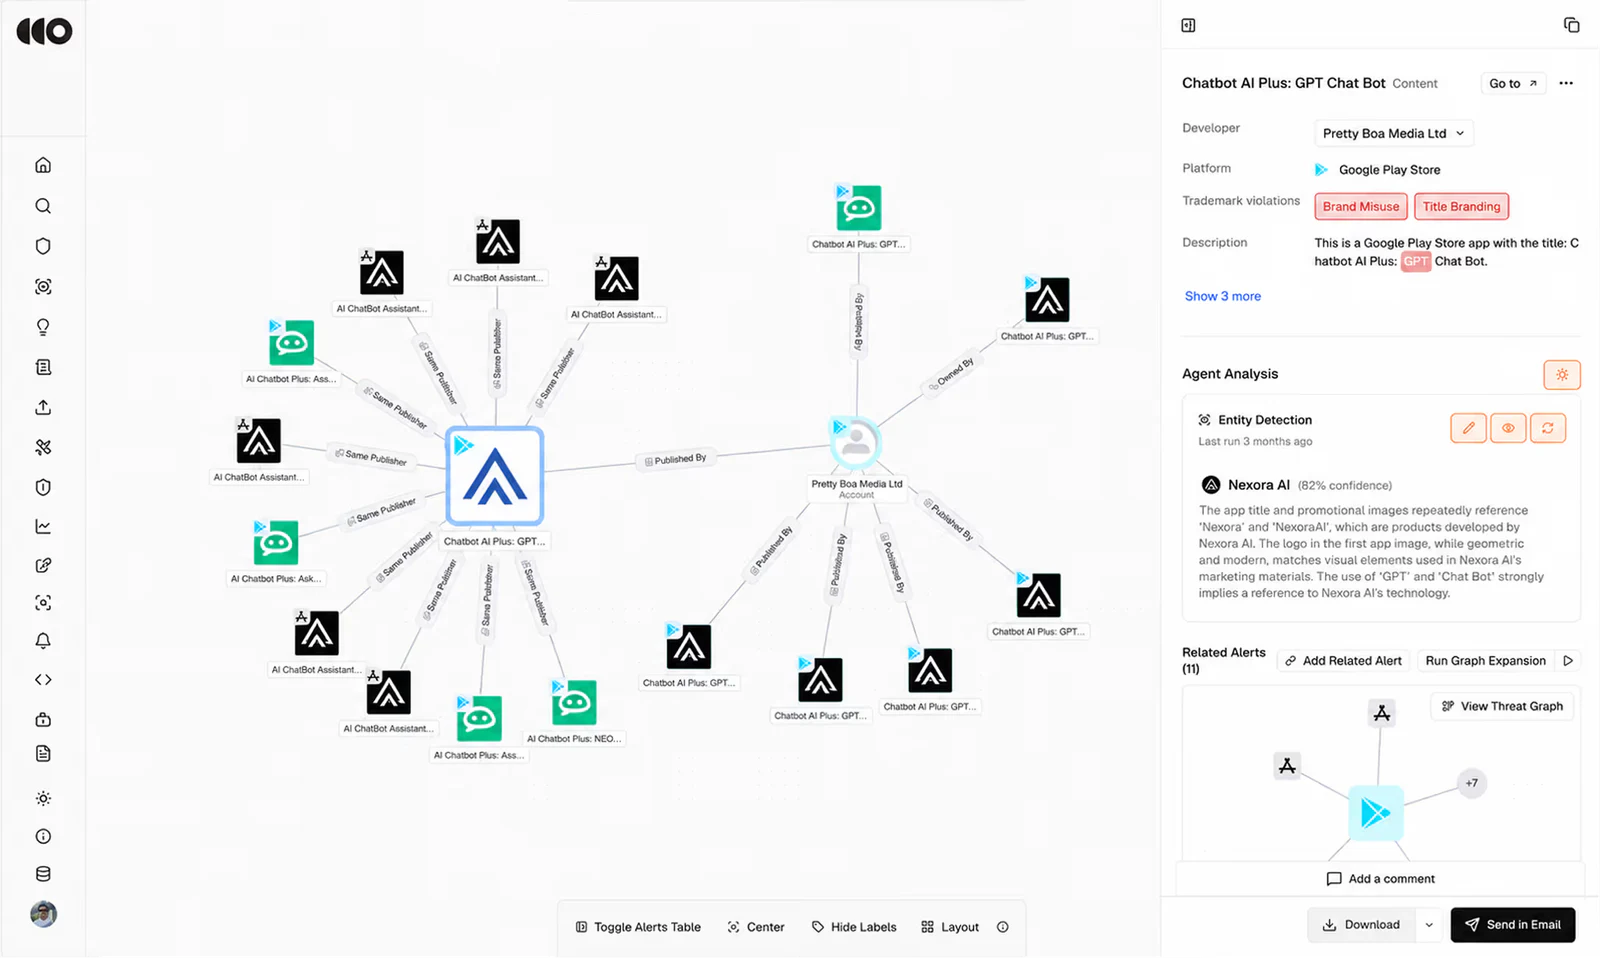
Catch fraud infrastructure before it reaches your queues as customer complaints, chargebacks and escalations.
Usually the operation behind it. Sister domains, ad accounts, social profiles and messaging groups often share the hosting and registration patterns of the domain your team reported, and they keep running after that one URL is gone. Outtake maps everything still connected to a closed case so it can be removed in the same pass.
Outtake detects the external scams that impersonate financial institutions: lookalike domains, cloned login portals, phishing kits, fake investment and trading platforms, executive and advisor impersonation, fraudulent ads, counterfeit mobile apps, fake customer support accounts and the dark web activity that connects them.
No. Outtake matches on logos, layouts and imagery, along with the relationships between entities tied to your institution. A cloned portal or a fake advisor profile gets flagged even when it never uses your exact name.
Takedowns are completed in hours, with a 99.4% confirmation rate. More than 90% of social takedowns are completed in under 24 hours. Recon Agent scans for new threats every 16 minutes, and Outtake sends takedown requests directly to registrars, hosting providers and platforms in parallel. Connected domains are filed together so the sister sites can be removed alongside the reported domain.
Outtake links related domains, accounts, apps, ads, wallets, hosting and operator signals in the Threat Graph. Analysts work the whole campaign as a single case and remove its assets together. Each takedown feeds the next detection cycle, so repeat operators are recognized faster.
Investment scams usually start with a social profile or ad, move the victim into a messaging group and end on a fake trading platform. Outtake follows that path from the first signal, linking the profiles, groups, platform domains and wallet infrastructure into one campaign so every piece can be removed.
No. Transaction monitoring, identity and device tools watch activity inside your environment. Outtake covers the sites, profiles, ads and apps scammers build outside it to reach your customers before a transaction happens. Fraud analysts use Outtake findings as early warning of campaigns that would otherwise surface later as complaints or chargebacks.
Outtake monitors social platforms including Meta, Threads, LinkedIn, X, TikTok and YouTube; messaging apps such as Telegram and WhatsApp; the Apple App Store and Google Play; domain registrars and hosting providers; Google and Bing search and their ad networks; and the dark web.
People working in fraud, cybersecurity, threat intelligence, brand protection and trust and safety use Outtake to investigate and remove external threats that target their institution and its customers.
GET A PERSONALIZED VIEW OF THE EXTERNAL THREATS TARGETING YOUR INSTITUTION.