Sean Sosnowski
Research Director, Software Analyst Cyber Research

Outtake calls its approach next-generation DRP. Sean Sosnowski examines the operating model behind that claim and how buyers can evaluate it.
A direct conversation with the analyst behind The Future of Digital Risk Protection Is External Trust Operations.
Watch the webinarResearch Director, Software Analyst Cyber Research
Head of Product Marketing, Outtake
had a material digital risk incident this year
cannot automatically stop a hijacked AI agent
trace an attack to the full campaign behind it
of observed attack techniques were bolstered by generative AI
84%, 96%, and 5%: 2026 Digital Risk Report. 15%: Verizon 2026 Data Breach Investigations Report, cited by SACR.
No deck. No product tour. Eight questions about the category reset and the claims buyers should test.
How external campaigns changed after the category formed.
What isolated alerts miss about the wider operation.
Why adding AI to monitoring does not change the operating model.
Business entities become the protected object. Campaigns become the unit of analysis.
One executive impersonation campaign traced through both workflows.
How DRP connects with threat intelligence, fraud, brand protection, and attack surface management.
The proof to ask for beyond a product demonstration.
What to do in the first 30, 60, and 90 days.
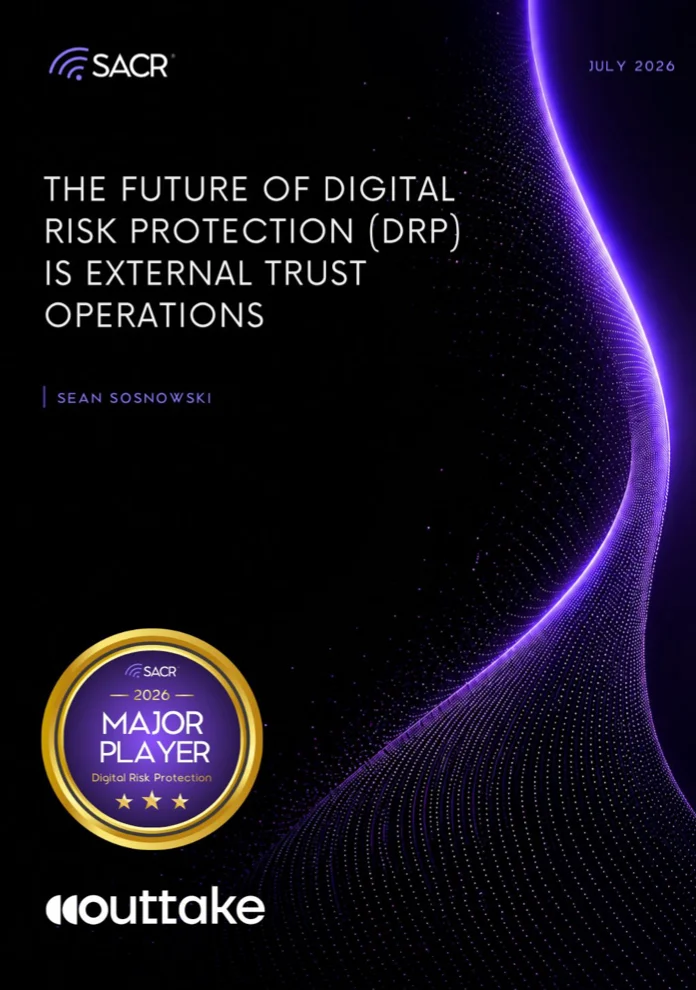
SACR defines External Trust Operations and gives buyers a framework for evaluating the category reset.
PDF · 21 pages · SACR · July 2026
An account can disappear while the domain network stays live. A phishing page can come down after credentials were collected. The artifact is gone. The operation may still be running.
Analysts monitor surfaces and file takedowns by hand.
Models flag likely abuse. Analysts still run each case.
The platform links the campaign, routes response, and verifies closure.
The question is which model your program actually runs.
Includes the recording and SACR's full 21-page report.