First-party warning / Undated
A published homoglyph example targets the corporate email domain
First American documents a fraudster changing @firstam.com to @first-arn[.]com, substituting ‘rn’ for ‘m’.
Outtake is an AI-native threat intelligence and Brand Protection platform. It finds the lookalike domains, spoofed escrow and closing emails, fake agent and branch identities, and fraudulent title and payoff instructions impersonating First American, investigates the infrastructure behind each one, and coordinates removal with the registrars, hosts, and mail providers keeping them running.
The public record is consistent: fake email identities, altered wiring instructions, seller impersonation, notary fraud, and AI-generated personas all target trust before funds move.
First American documents a fraudster changing @firstam.com to @first-arn[.]com, substituting ‘rn’ for ‘m’.
First American says it will not request passwords or personal financial information by email and directs recipients to verify changed payment or wire instructions with their representative.
First American research describes deepfake audio or video impersonating real estate professionals and home sellers.
The Agency Division launched an identity verification capability against a growing real estate fraud threat.
First American launched free title monitoring and fraud alerts as an early warning system for property owners.
Agency guidance names seller impersonation, wire and email spoofing, payoff fraud, notary and ID fraud, and deepfake impersonation among recurring schemes.
A customer or agent trained to accept mail and logins across two root domains and a dozen subdomains has no reliable way to spot a thirteenth that is fake.
Escrow officer email, payoff letters, wiring instructions, and closing document delivery carry the transaction. First American’s own guidance warns that the instruction itself can be forged.
Policy-issuing agents, local branch and escrow officer identities, notaries, and vendors all become identities a fraudster can imitate.
Title monitoring enrollment, home buying guidance, property-owner identity, and seller verification extend trust into consumer-facing journeys.
Two root domains and a dozen subdomains train customers and agents to accept many legitimate destinations, while homoglyphs imitate the pattern.
Cross-surface detection, autonomous investigation, campaign correlation, and provider coordination stay in one workflow, so separate teams can work from the same evidence and response path.
Outtake combines entity definition, agentic search, threat-graph intelligence, and provider-level response coordination in one platform. The result is a continuous external-risk workflow that gets more context from every investigation.
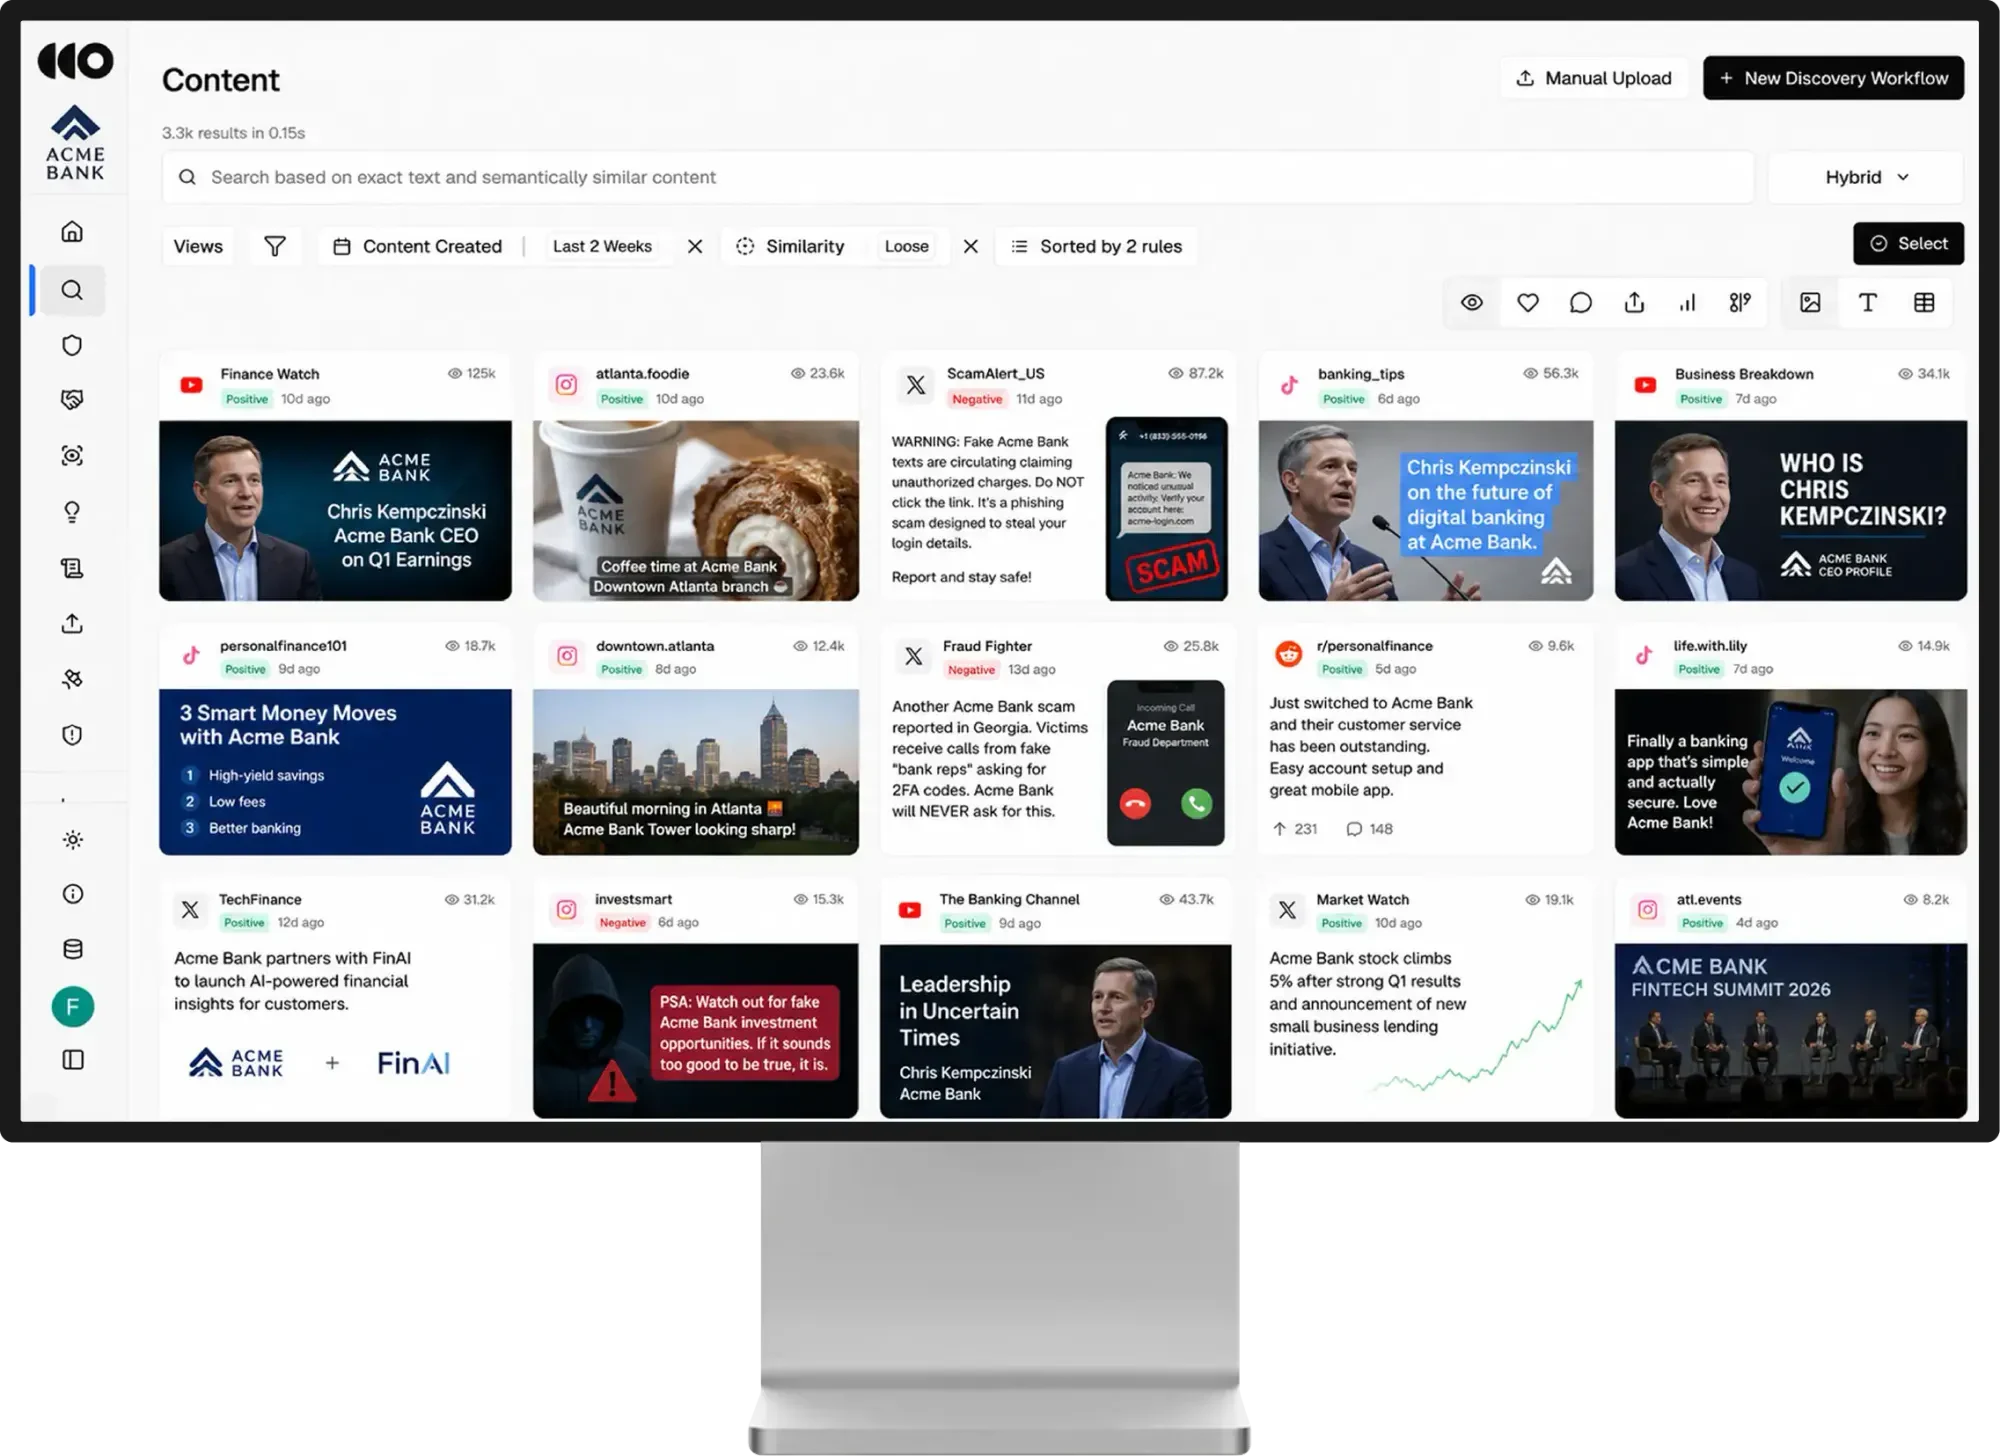
Outtake models the First American names, domains, visual identities, portals, branches, agents, and transaction surfaces that legitimate customers and partners are expected to trust.
Autonomous agents look across domains, ads, social platforms, apps, messaging, and other external surfaces for copied identity, altered language, visual similarity, and suspicious transaction cues.
Registration, hosting, certificates, mail configuration, templates, and delivery paths are connected into a graph that helps teams see related activity instead of isolated alerts.
Provider-level response paths support coordinated action at the source dependencies. Each investigation adds evidence that can improve how related activity is detected, prioritized, and handled over time.


In 30 minutes, see how Outtake finds a lookalike of a First American closing domain, investigates the infrastructure behind it, connects it to related activity across agent, closing, and consumer channels, and coordinates action with the providers keeping it online.